Security health check
A structured look at accounts, devices, email, backups, the network edge and the people who approve payments, ranked by what to fix first.
Fixedfrom $2,400
We check your systems, train your people and write the plan for a bad day, then explain every finding in words a board can act on. No scare stories, no products to sell, and a fixed price agreed before any testing starts.
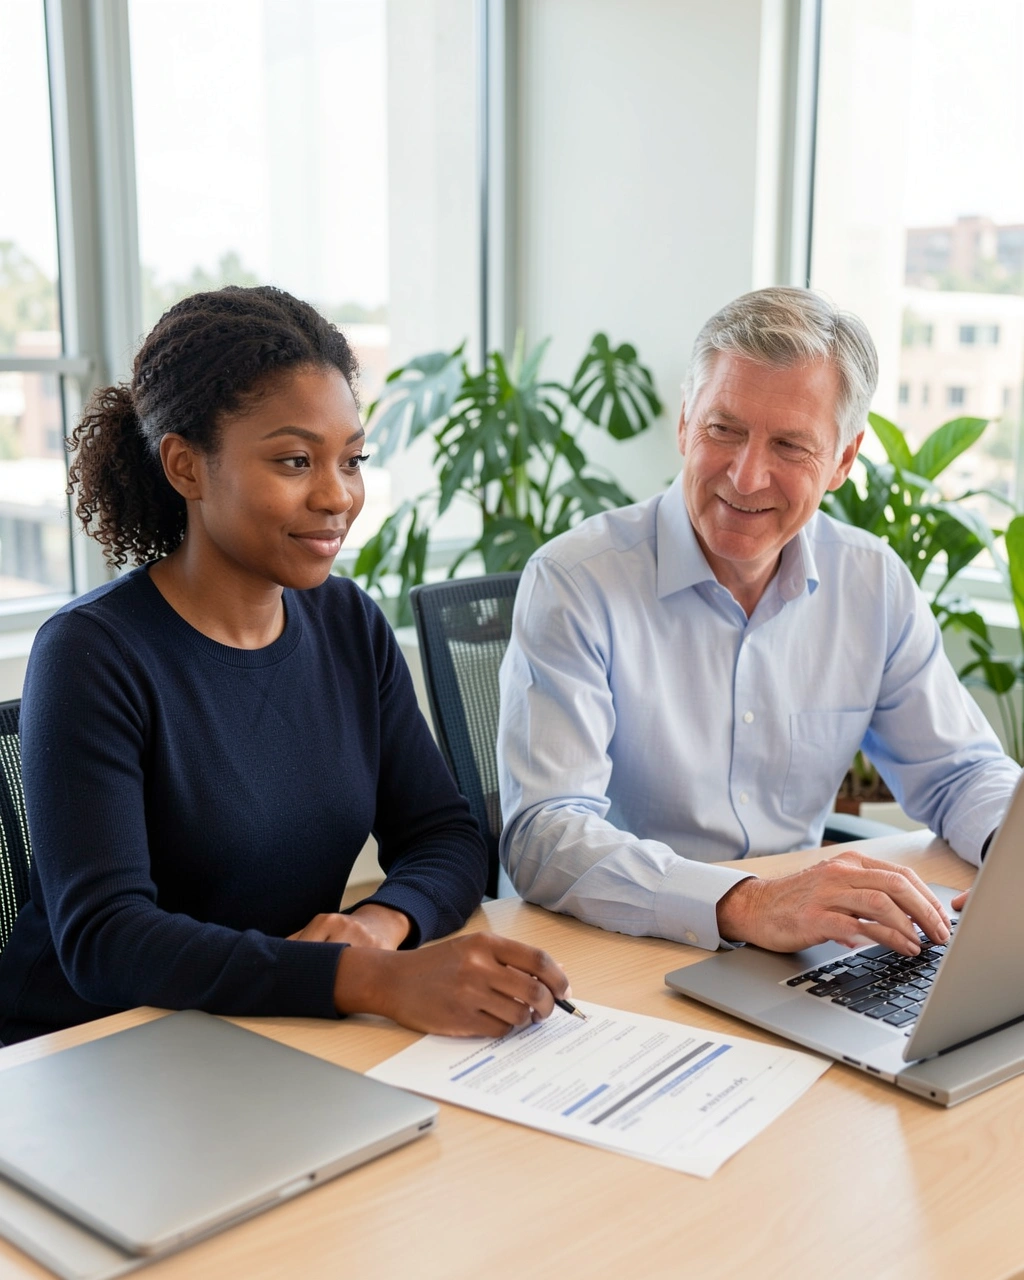
Each piece of work can stand alone, though most clients start with a health check and decide the rest from what it finds.
A structured look at accounts, devices, email, backups, the network edge and the people who approve payments, ranked by what to fix first.
Your website, customer portal or office network tested by a consultant trying the routes an attacker would, within limits a director signs off in writing.
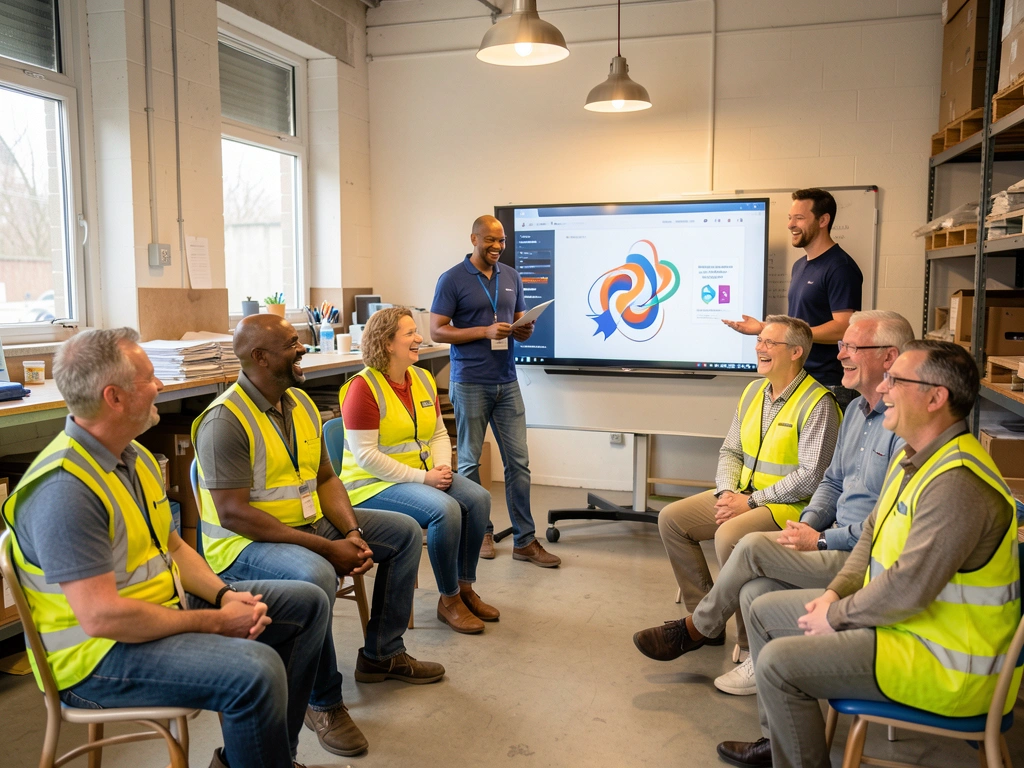
Short, good humoured sessions on suspicious emails, payment fraud by phone and safe working away from the office, with examples from your own sector.
Who decides, who calls whom and what gets switched off first, written as a short plan and rehearsed in a two hour tabletop exercise.
Help answering the security questions that customers, insurers and auditors send, honestly and with the evidence ready to hand.
A named consultant who joins your management meeting each month, reviews new systems and answers questions before they turn into problems.
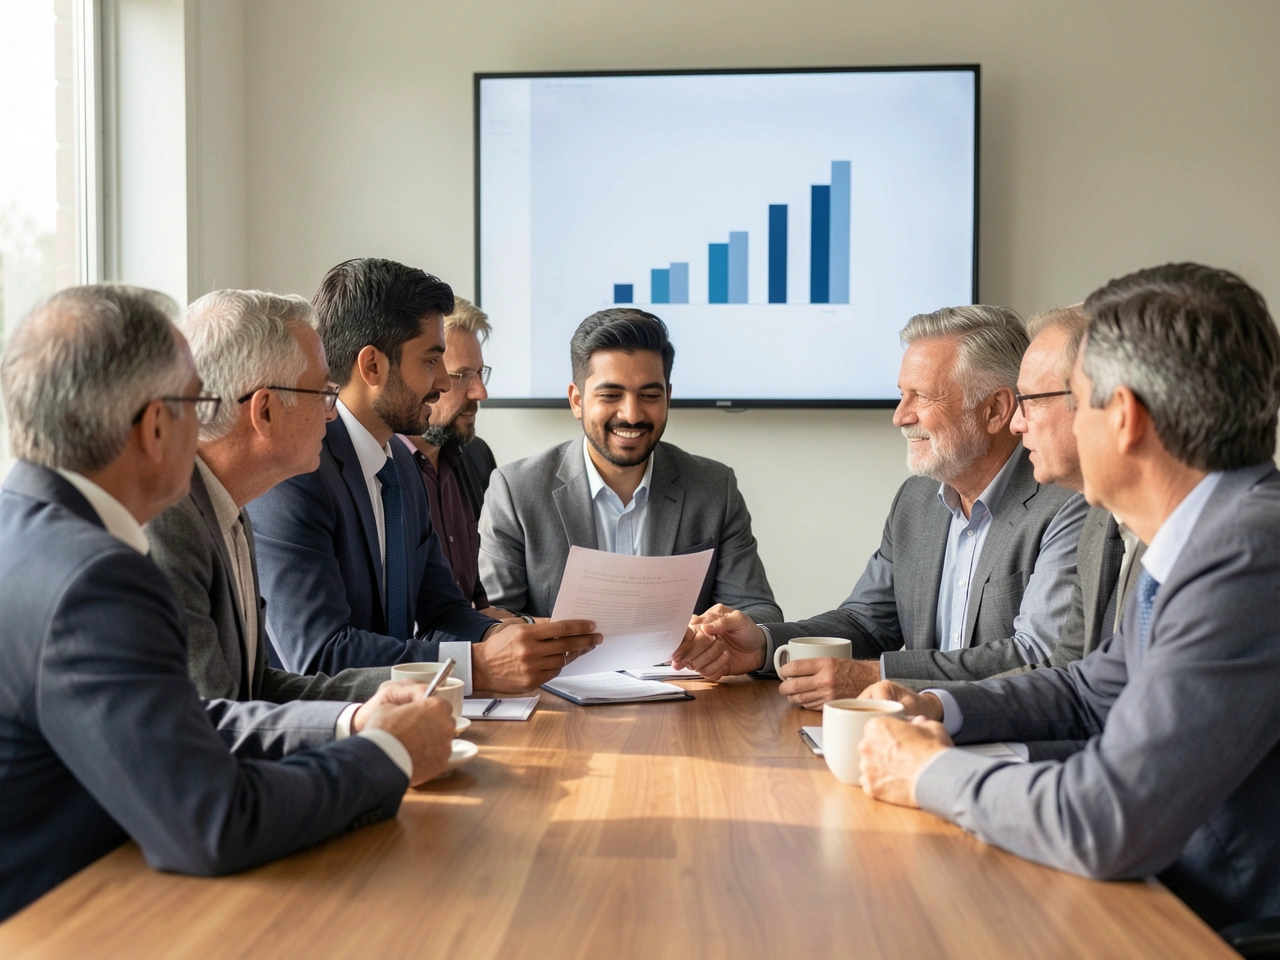
Every finding is written twice: once in plain words for directors, saying what could happen and how likely it is, and once in technical detail for whoever fixes it. Nothing is described as more alarming than it is.
Findings are sorted into three lists, this week, this quarter and this year, so the most useful fixes happen first and the budget can follow.
Six areas, chosen because they cover the ways companies of 10 to 250 people most often run into trouble. Data protection and reporting rules vary by country, so the report notes which findings may matter to your regulator.
| Area | What we check | What you receive |
|---|---|---|
| Accounts and sign in | Which accounts use two step sign in, who holds admin rights and whether former staff can still log in | A list of accounts to close, tighten or protect |
| Laptops and phones | Updates, disk encryption, screen locks and what happens when a device goes missing | A device by device table with the gaps marked |
| Settings that stop others sending mail in your name, and forwarding rules nobody remembers creating | The exact settings to change, written for your IT provider | |
| Backups | Whether a copy sits apart from the main systems, and whether a restore actually works | The result of a test restore we watch you run |
| The network edge | Remote access, open services and the office router, scanned from outside with your permission | Each exposed service with a fix or a reason to keep it |
| Money and people | Who can change bank details or approve payments, and how such requests are checked | A simple call back rule for payment changes |
Testing starts only once a director has signed the scope and the dates. We never test systems you do not own or have permission to test.
Prices are fixed for the scope agreed on the first call and shown here as examples in US dollars. If something needs more time than planned, we stop and ask before doing any extra work.
fixed, from$2,400
fixed, from$3,900
a month, from$1,150
We sell no software or hardware and take no fees from vendors, so every recommendation is made on its merits alone.
Thirty minutes on how the company works, which systems matter most and what, if anything, is worrying you.
A director signs the scope, the dates and the name of the person who can pause testing at any moment.
Interviews, settings reviews and scans over five to ten working days, timed around your busy periods.
We walk your team through the report, answer questions and agree who fixes what, and by when.
Thirty days later we check the urgent fixes and update the report, so the board can see the progress.
The checks are designed to be gentle, and anything with even a small risk of disruption is scheduled outside working hours with your agreement. A named person at your company can pause testing at any point.
No. We take no commission from vendors and resell nothing. If a tool is worth buying, we explain why, and you choose where to buy it.
We stop, call the contact named in the scope the same day and help decide the next step. Serious findings never wait for the final report.
Rarely. We look at how data is protected, not at the data itself, and anything we do see stays confidential under the agreement signed before we start.
It helps, but compliance depends on the rules for your sector and country. The report flags findings likely to matter to a regulator or insurer, and we can work alongside your legal adviser.
Call rather than using the form. We help you contain the problem and keep the evidence, and we tell you whether you should also inform your bank, your insurer, the police or a regulator, because reporting rules differ from country to country.
We expected a lecture and a sales pitch. Instead we got a ten minute summary for the partners, a list for our IT provider and a retest showing every urgent item closed.
The training was the first our team actually enjoyed. A fortnight later someone in accounts spotted a fake change of bank details and phoned the supplier to check before paying.
The tabletop exercise showed that nobody knew who could take the booking system offline. That gap is closed, and the whole plan now fits on two pages.
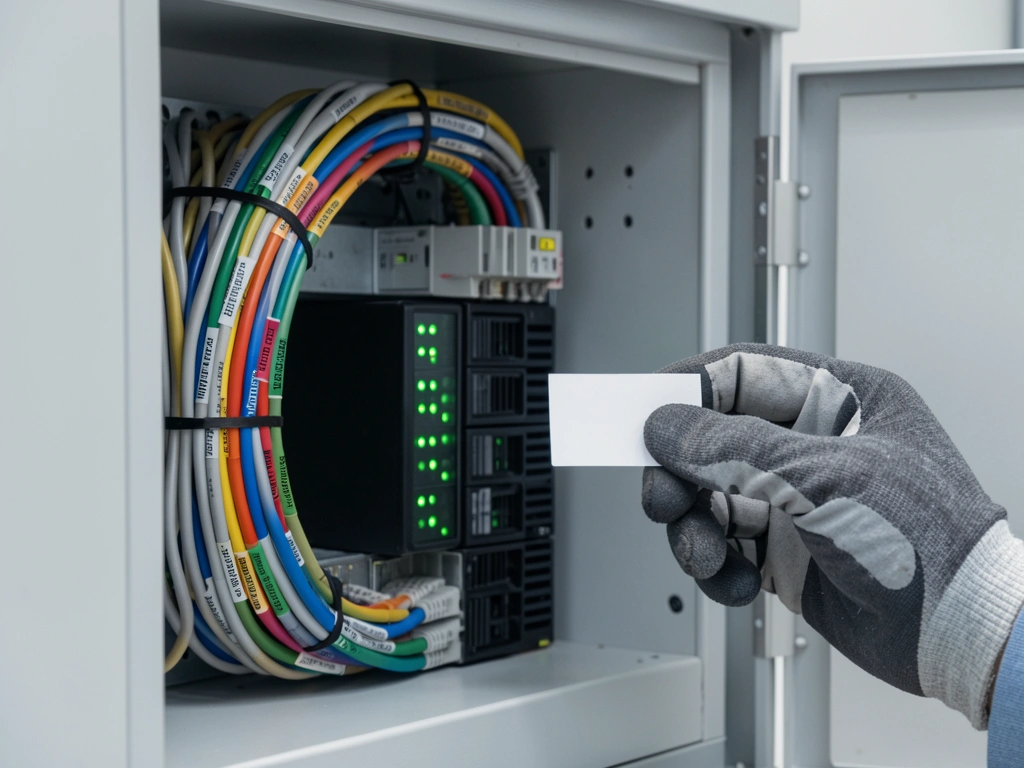
Photographed at client sites with permission, with screens and documents kept out of shot.
Tell us a little about the company and what prompted you to get in touch. A consultant answers within one working day and offers a slot for the scoping call.
Please do not send passwords, network details or anything sensitive through this form. We gather what we need after the scope is signed.
On site within about two hours of the city, and remote work for clients anywhere
| Monday to Friday | 08:30 to 18:00 |
| Testing windows | Evenings and weekends by agreement |
| Retainer clients | Incident line at any hour |
Phone us rather than sending the form. Unless your IT provider advises otherwise, keep affected machines switched on but disconnected from the network, and write down what you noticed and when.
Call +44 20 7946 0246This cybersecurity consultant website was built by AI from two sentences. Tell us about your business and yours is built the same way, with its pages, photos and booking in place, ready to preview in minutes.
About this sample page
Lockstep Cyber Security is an invented consultancy, and its one page sketches how a calm security practice could present itself on AI Web Maker. A shield draws its tick on the opening photo beside a headline that promises clarity instead of threats. Services, a board friendly report and a table of six checked areas follow before any price appears. Three fixed prices, five steps to a retest and six plain questions come next. The order lets a director understand the work fully before deciding whether to pay for it.
A consultancy using AI Web Maker describes its checks, its clients and its pricing, then edits the draft page and enquiry form that the builder returns. Hosting a live page is $119 for the year or $19 per month, the domain is extra, and drafts and previews are never billed. Lower on this sample page, short notes cover why the page avoids fear, how findings are written for two readers and why consent appears as a step. They also cover the statement of independence from vendors and the safety notes on the form. A real firm could keep this structure and replace every price, photo and review with its own.
The whole sample website of a cybersecurity consultant, explained ·